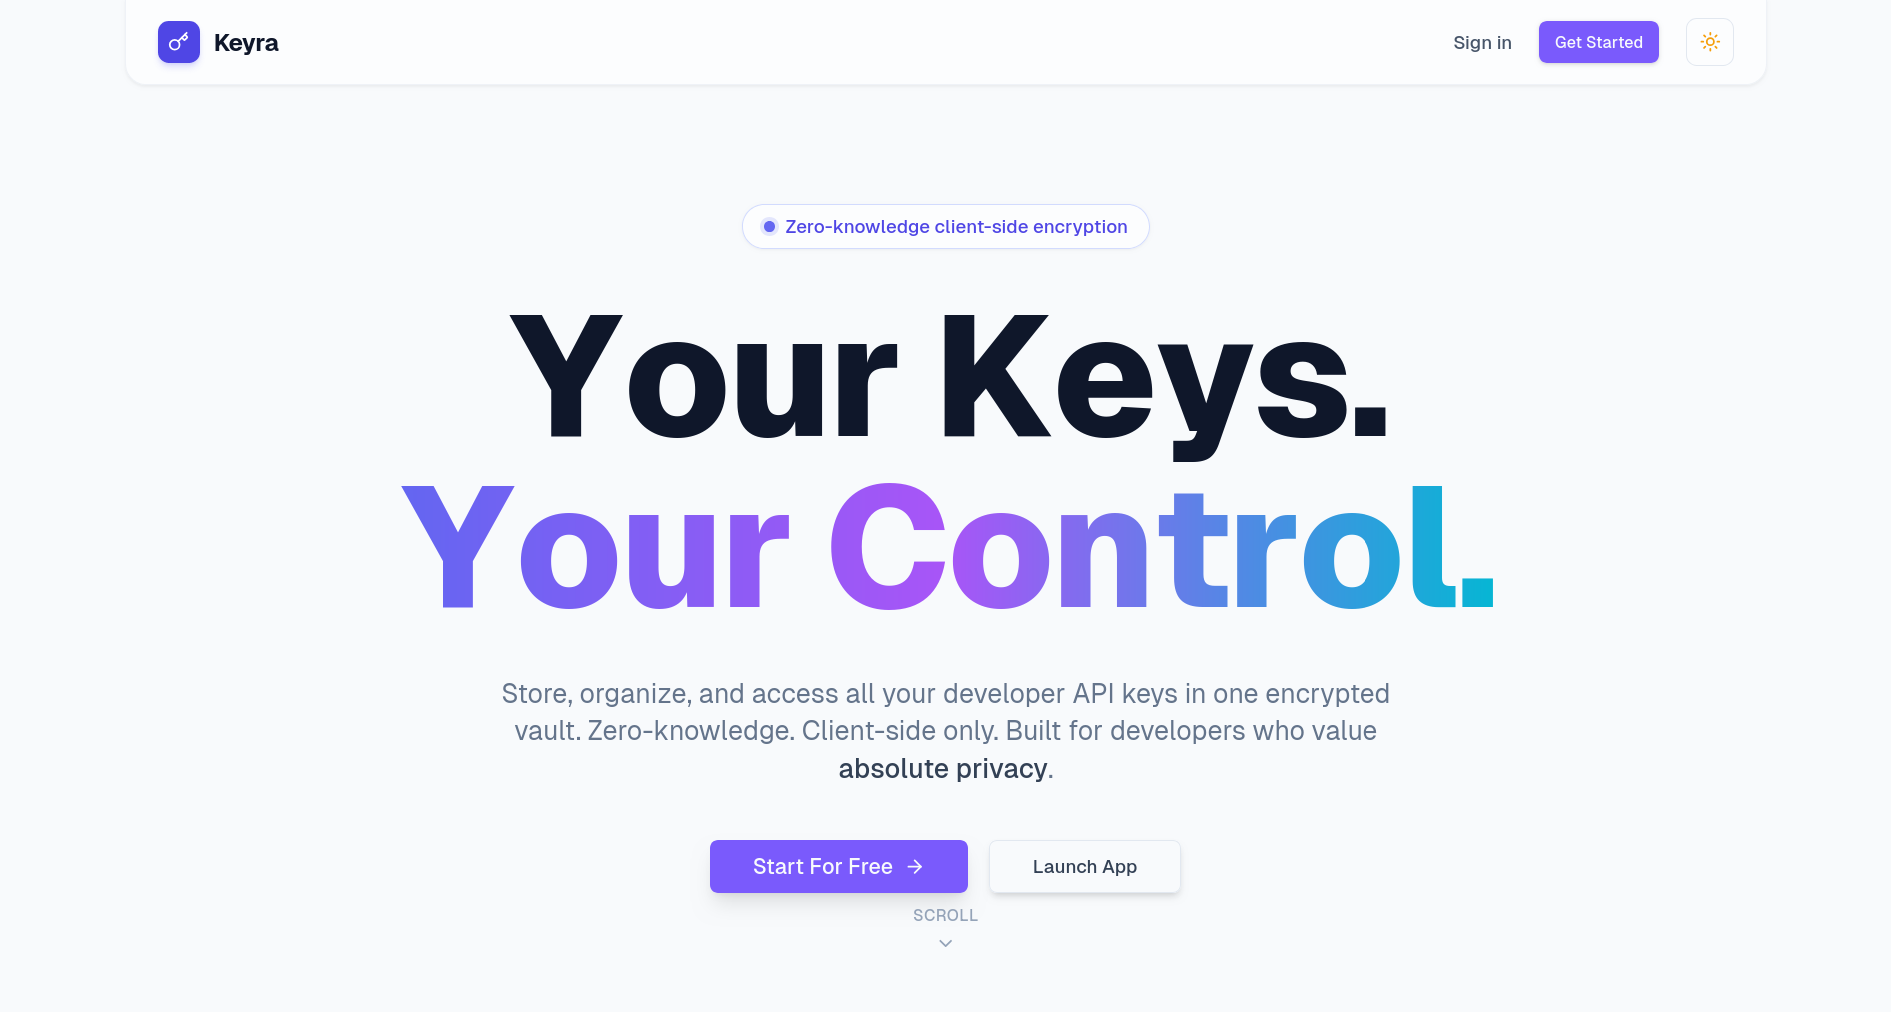
Keyra provides developers with a secure, beautifully animated vault for their API keys. Everything is encrypted locally in the browser using AES-256-GCM, meaning the servers never see the plaintext keys or the master password.
// Input_Challenge
Developers often store sensitive API keys in plain text, fragmented across local files, or rely on cloud providers where they have to trust the provider's server-side encryption and security practices.
// Output_Logic
Engineered a client-side encryption pipeline using the Web Crypto API, PBKDF2 for key derivation, and AES-256-GCM for encryption. Built a premium animated UI with Next.js, Tailwind CSS, GSAP, and Framer Motion. Implemented team sharing using RSA-OAEP public key infrastructure (PKI) backed by Supabase.
_frontend
_backend
_tools
Successfully implemented a complex client-side encryption and PKI sharing architecture natively in the browser.
Delivered a premium user experience combining GSAP scroll animations, Aurora backgrounds, and Framer Motion.
Ensured absolute data privacy where even the database administrators cannot read the stored API keys.